RU | EN
Get in touch
v.2026 Infrastructure for non-standard tasks

Where others
say "not supported" —
we launch it.

Megatel is an engineering workshop for projects that don't fit standard data center plans. Legacy stack, porting of old software, cyber incident investigation and data recovery after ransomware.

  • [✓] Any versions of PHP / Perl / Python / MySQL
  • [✓] Legally clean reverse engineering per client specs
  • [✓] Incident response — from 48 h.
18+ years in the field
99.99% uptime SLA
// Core directions

Four sectors of engineering work

Each direction is about restoring control over what is considered "unsupported" or "lost".

01 HOSTING / LEGACY

Hosting for non-standard projects

We run what no standard shared hosting can. Any exotic and outdated versions of PHP, Perl, Python, ASP-classic, MySQL and PostgreSQL — isolated, with dedicated IPs, daily backups and FS-level rollback.

  • PHP 4.4 → 8.x  ·  Perl 5.005 → 5.30
  • Python 2.4 / 2.7 / 3.x  ·  Ruby 1.8+
  • MySQL 4.0+  ·  PostgreSQL 7.4+  ·  Firebird
  • Containerization in LXC/Docker without losing compatibility
02 REVERSE / PORTING

Legal reverse engineering

We port software written for DOS, Windows 95/98, Novell NetWare, TR-DOS, CP/M and other historical platforms to modern operating systems — including adaptation for Linux. We work strictly within the law and upon written authorization from the rights holder.

  • Analysis of data formats, protocols and file structures
  • Core rewrite on supported compilers
  • Compatibility with modern drivers and networking
03 FORENSICS / IR

Infection and compromise analysis

We reconstruct the attack timeline: exactly how the intrusion occurred, which accounts and services were involved, what data was exfiltrated. We prepare a closing report with indicators of compromise and a root cause remediation plan.

  • Triage of servers and workstations
  • Artifact analysis: memory, logs, registry, FS
  • Network timeline and IOC per MITRE ATT&CK
  • Hardening and segmentation recommendations
04 RECOVERY / DECRYPT

Data recovery after ransomware

We help recover data encrypted by cyber extortionists — where technically possible: cryptographic implementation vulnerabilities, surviving keys in memory, shadow copies, backups outside the perimeter. No intermediaries and no negotiations with attackers.

  • Ransomware family identification and weak point analysis
  • Recovery from shadow copies and remnant data
  • File carving, partial database recovery
  • Safe re-entry into infrastructure after incident
// Supported stack

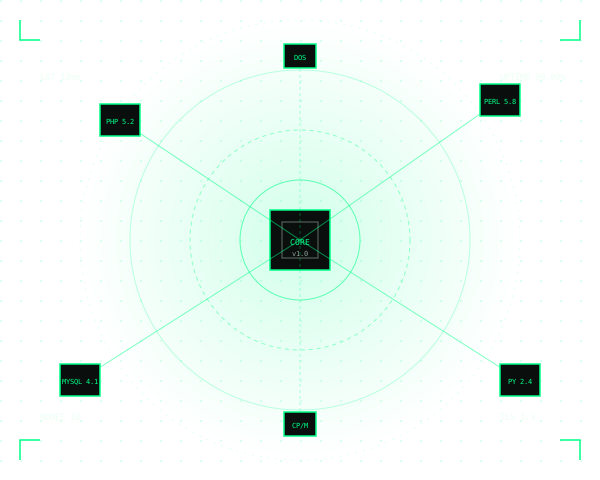
We'll run almost anything that once worked

If your project uses an interpreter version that hasn't been available from any mainstream hoster for years — that's no reason to rewrite it from scratch. We set up an isolated stack, maintain it in working condition, and develop a gradual migration plan — only when you're ready.

// How we work

Process — transparent and documented

  1. /01

    Briefing

    A free technical conversation: what you have, what you need, what the constraints are. The outcome is a brief summary with diagnosis and options.

  2. /02

    Audit & Assessment

    We take images, read artifacts, reverse-engineer formats. We scope the work and provide a fixed quote — or an hourly rate for research tasks.

  3. /03

    Implementation

    Isolated environment, regular demos, a shared channel for questions. All code and all artifacts are yours from the moment the contract is signed.

  4. /04

    Handover & Support

    Documentation, runbook, team training. Ongoing support — optional: one-time, subscription, or on-call.

18+ years of engineering experience
240+ ported applications
99.99% infrastructure uptime
48 h IR team response time
// What we believe is right

Legacy software is not garbage. It's an asset that outlived its authors.

We don't try to talk clients into "rewriting everything from scratch on a modern framework". Usually that's more expensive, slower, and riskier than it seems. We help preserve the working logic that generates revenue, and carefully migrate it to a place where it will run for another 15 years.

In reverse engineering, we work only with documented rights — your own software, inherited, purchased, or transferred by contract. No pirated keys, no license bypasses, no cracking others' software. In forensics — defense only, never offense.

// Contact

Describe your task — get a technical answer, not a presentation

Your initial inquiry is answered by an engineer, not a sales manager. If the task is outside our expertise — we'll say so honestly and recommend colleagues.

EMAIL
RESPONSE SLA within 1 business day
IR HOTLINE 24 / 7 for active incidents